

Trust Modernization series: Phase 1: Roadmap to Cryptographic Visibility
Every post-quantum migration runs through the same chokepoint: nobody actually knows where all the cryptography is.
It lives in identity systems, cloud platforms, vendor appliances, machine identities, and software supply chains. No single team owns it, and no single system of record describes it.
Today, STOPSO is releasing the second paper in our Trust Modernization series: Phase 1: Roadmap to Cryptographic Visibility, by Jason Sidler and David Wilkinson.
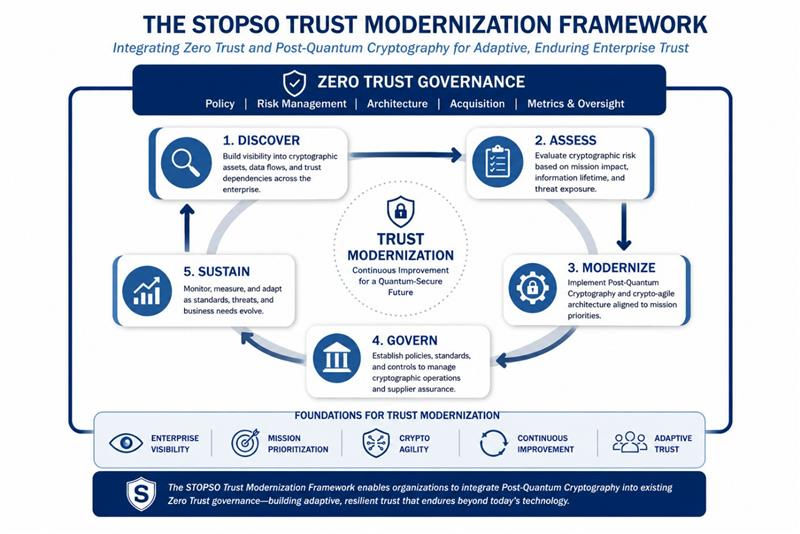
Our first paper established the Trust Modernization Framework. This one makes its first phase, Discover, actionable: what an organization must find, record, and be able to prove before it can prioritize a single migration decision.
The central argument: do not build another inventory. Extend the enterprise visibility you already have, treat cryptography as a first-class attribute of every asset, and maintain the Cryptographic Bill of Materials as a living evidence base, with every value carrying its source, timestamp, and confidence, and every gap recorded as deliberately as every fact.
With CISA and NIST directed to publish government-wide CBOM guidance by early 2027, the inventory you build today is the artifact federal expectations will attach to tomorrow.


Comments